Securing Automated Static Site Deployments
Learn how to prevent corrupt Markdown and broken image assets in automated publishing pipelines by implementing strict byte-level validation and deployment contracts.
Table of Contents5 sections
A working view of Securing Automated Static Site Deployments: A phone, test checklist, and laptop arranged for Android release readiness.
When an automated publishing pipeline fails, the symptoms are often frustratingly opaque. A scheduler might inadvertently write a binary PNG payload into a Markdown article path, or commit a truncated 34-byte hero asset that fails to render. These errors lead to 404 responses for new content, while existing canonical articles remain healthy. The core problem is that file extensions are not content-type guarantees. Relying on naming conventions alone allows malformed data to enter your repository, leading to build failures that are difficult to Debug Broken Links Deployment Flows after the fact. To maintain a stable site, you must treat every automated write as a potential point of failure and implement a strict contract for how content and assets are handled.
Diagnosing Byte-Level Corruption
The primary cause of these failures is a mismatch between the expected data format and the actual bytes written to the repository. In many automated workflows, a scheduler interacts with the GitHub API to push content. If the encoding logic is flawed, binary data can be treated as text, or vice versa. For Diagnosing Factory Instance Creation Issues, if a process attempts to commit a hero image but fails to encode it correctly, the resulting blob might be a truncated byte stream. When the static site generator attempts to process this, it encounters an invalid file format. Because the file exists in the repository, the build process may not throw an immediate error, but the resulting HTTP response for that asset will be a 404 or a corrupted binary stream. Inspecting the latest publication commits is the first step in diagnosis. Look for files where the byte count is suspiciously low or where the file content contains base64-encoded binary data instead of expected YAML frontmatter or Markdown text.
Establishing a Strict Promotion Contract
To prevent these issues, you must enforce a strict separation of concerns within your repository structure. Store UTF-8 Markdown files exclusively under a dedicated content directory, such as content/articles/, and restrict binary assets like PNG, JPEG, or WebP files to a public/assets/ directory. This physical separation allows your CI/CD pipeline to apply different validation rules based on the file path. When using the GitHub API, explicitly define the encoding for each blob. Use utf-8 for text-based files and base64 for binary assets. By enforcing this at the API level, you reduce the risk of binary data being misinterpreted as text. Furthermore, implement a validation layer that checks the file signature (magic bytes) before the commit is finalized. If a file is intended to be a PNG, the first few bytes must match the PNG header. If the signature is missing or incorrect, the promotion should be rejected immediately.
Implementing Preflight Validation Checks
Validation should not be limited to the file format. A publication is not truly ready until the article, its associated metadata, and every referenced asset are verified as accessible. Before moving a draft to a published state, your pipeline should perform a series of preflight checks. First, verify the SHA-256 hash of the generated assets to ensure they match the source. Second, perform a dry-run build in a temporary environment to confirm that the static site generator processes the new files without warnings or errors. Finally, use a script to perform a live HTTP request to the staging URL of the new content. If the article or any referenced hero image returns anything other than an HTTP 200 status code, the deployment must be halted. This prevents broken content from ever reaching the production environment, ensuring that your site remains consistent and reliable for users.
Managing Promotion Queues and Duplicates
Automated schedulers often run in parallel or retry on failure, which can lead to duplicate or conflicting promotions. A common mistake is to allow a failed or duplicate promotion to move the source or draft out of its queue. Instead, implement a quarantine mechanism. If a promotion is identified as a duplicate or contains malformed data, it should be moved to a quarantine state for manual review rather than being discarded or partially deployed. This allows you to inspect the failed payload without losing the context of why the failure occurred. By keeping the source and draft in their original queue until a successful deployment is confirmed, you ensure that the state of your repository remains a single source of truth. This approach also simplifies the cleanup process, as you can easily identify and remove orphaned assets or quality records associated with the failed promotion.
Ensuring Deployment Integrity
Once the validation and quarantine logic are in place, the final step is to integrate these checks into your CI/CD pipeline. Use a comprehensive suite of commands to verify the integrity of the entire site. This should include linting the Markdown, testing the build process, and running a final verification step against the generated distribution files. For example, a standard verification script might look like this:
npm run validate
npm test
npm run check
npm run build
npm run verify:dist
Each of these steps serves a specific purpose: validation checks for syntax errors, testing ensures logic remains sound, and the final verification confirms that the output files are correctly formatted and accessible. By running these checks in a CI environment, you ensure that every deployment is consistent and that any corruption is caught before it impacts the production site. If the CI run fails, the pipeline should exit with a non-zero status, preventing the deployment from proceeding. This rigorous approach to automated publishing transforms your pipeline from a source of potential instability into a robust system that guarantees the quality and integrity of your content.
Continue Exploring
You Might Also Like
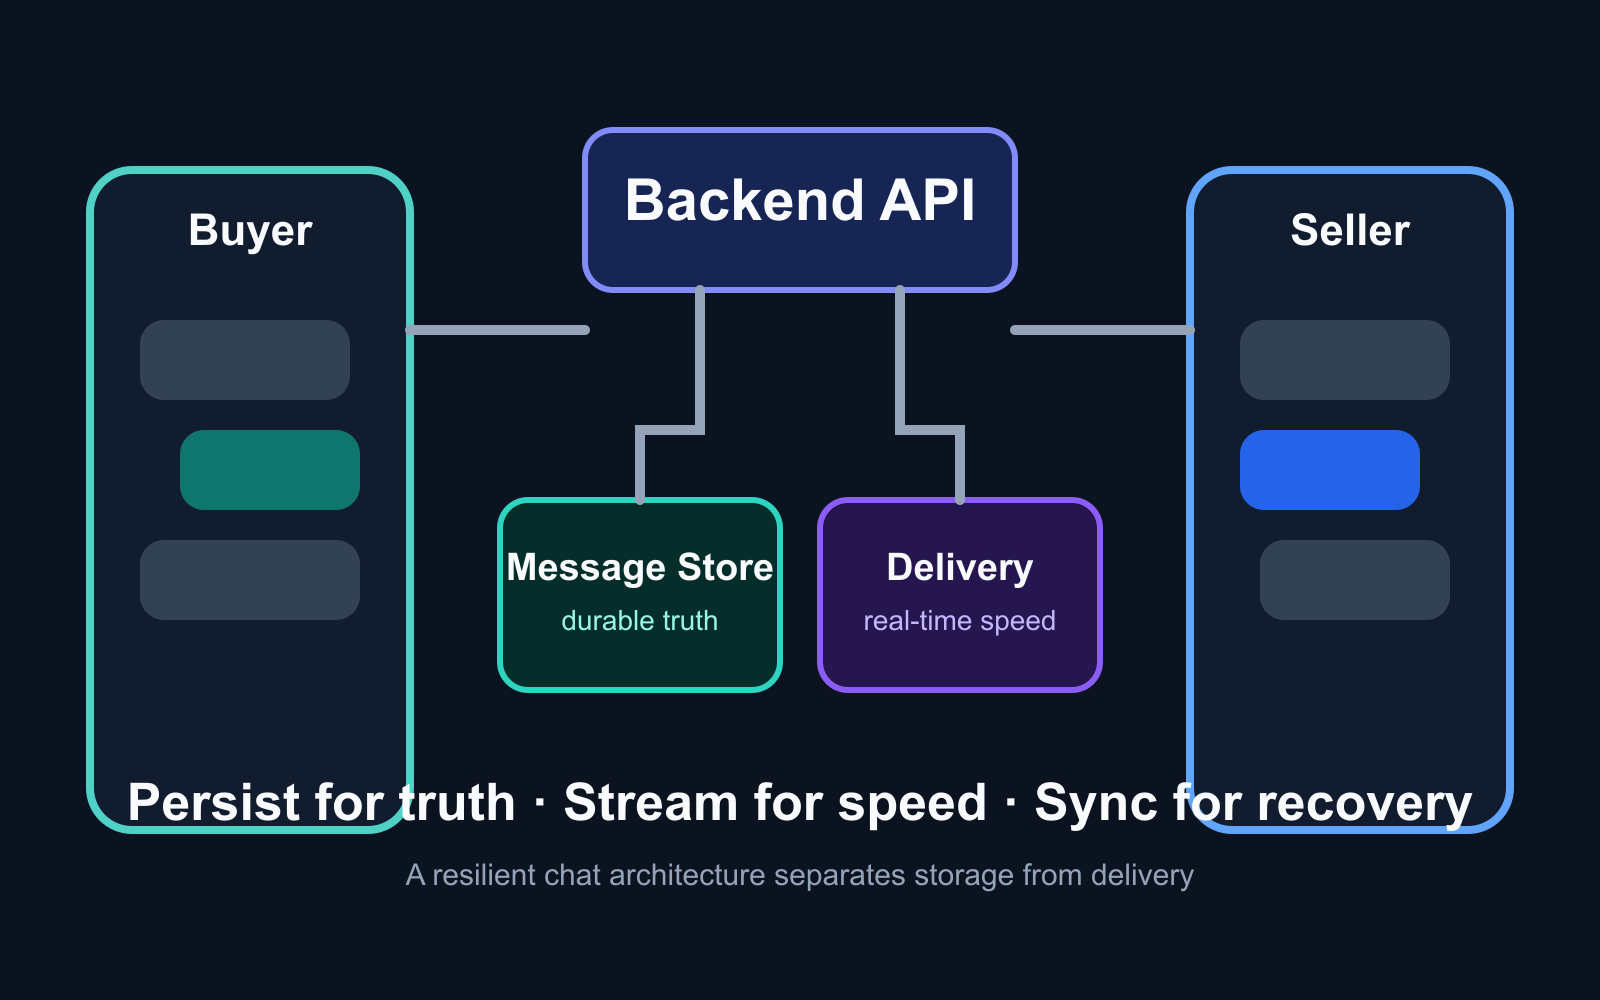
Chat App Architecture: Separate Delivery from Storage
Design a chat system that treats message persistence, real-time delivery, retries, ordering, and presence as separate responsibilities instead of one fragile socket flow.
Building an Isolated Linux Lab in VirtualBox
Learn how to build a safe, isolated Linux and Kali Linux laboratory in VirtualBox, focusing on network modes, safe snapshot workflows, and security boundaries.
Configuring HTTP Caching for Modern Web Applications
Learn how to choose safe HTTP caching headers for static websites and CDNs by mastering Cache-Control directives, content-hashed filenames, and validation.