Shift Left AI Coding Agent Boundaries with Pre-Commit Gates
Discover how engineering teams shift boundary enforcement left in AI coding agent pipelines to catch cross-module import leaks before commit time.
GitHub Actions workflows, build caching, automated verification gates, release tagging, and safe edge deployment pipelines.
Discover how engineering teams shift boundary enforcement left in AI coding agent pipelines to catch cross-module import leaks before commit time.
Learn how the Google Services Gradle plugin matches build variants to configuration files, where variant-specific JSON files live, and how to verify that your CI pipeline exercises the intended Firebase project.
Diagnose and resolve cross-platform npm ci EBADPLATFORM failures caused by lockfiles generated inside symlinked local node_modules directories.
Fix SonarCloud LCOV import failures when report paths drift in monorepos by aligning working directories, root resolution, and source file references.
Build a layered image gate that checks signatures, dimensions, byte hashes, decoder health, pixel anomalies, manifests, and the live deployed asset.
Diagnose missing and mismatched dependency checksums, regenerate Gradle verification metadata safely, and keep CI supply-chain protection enabled.
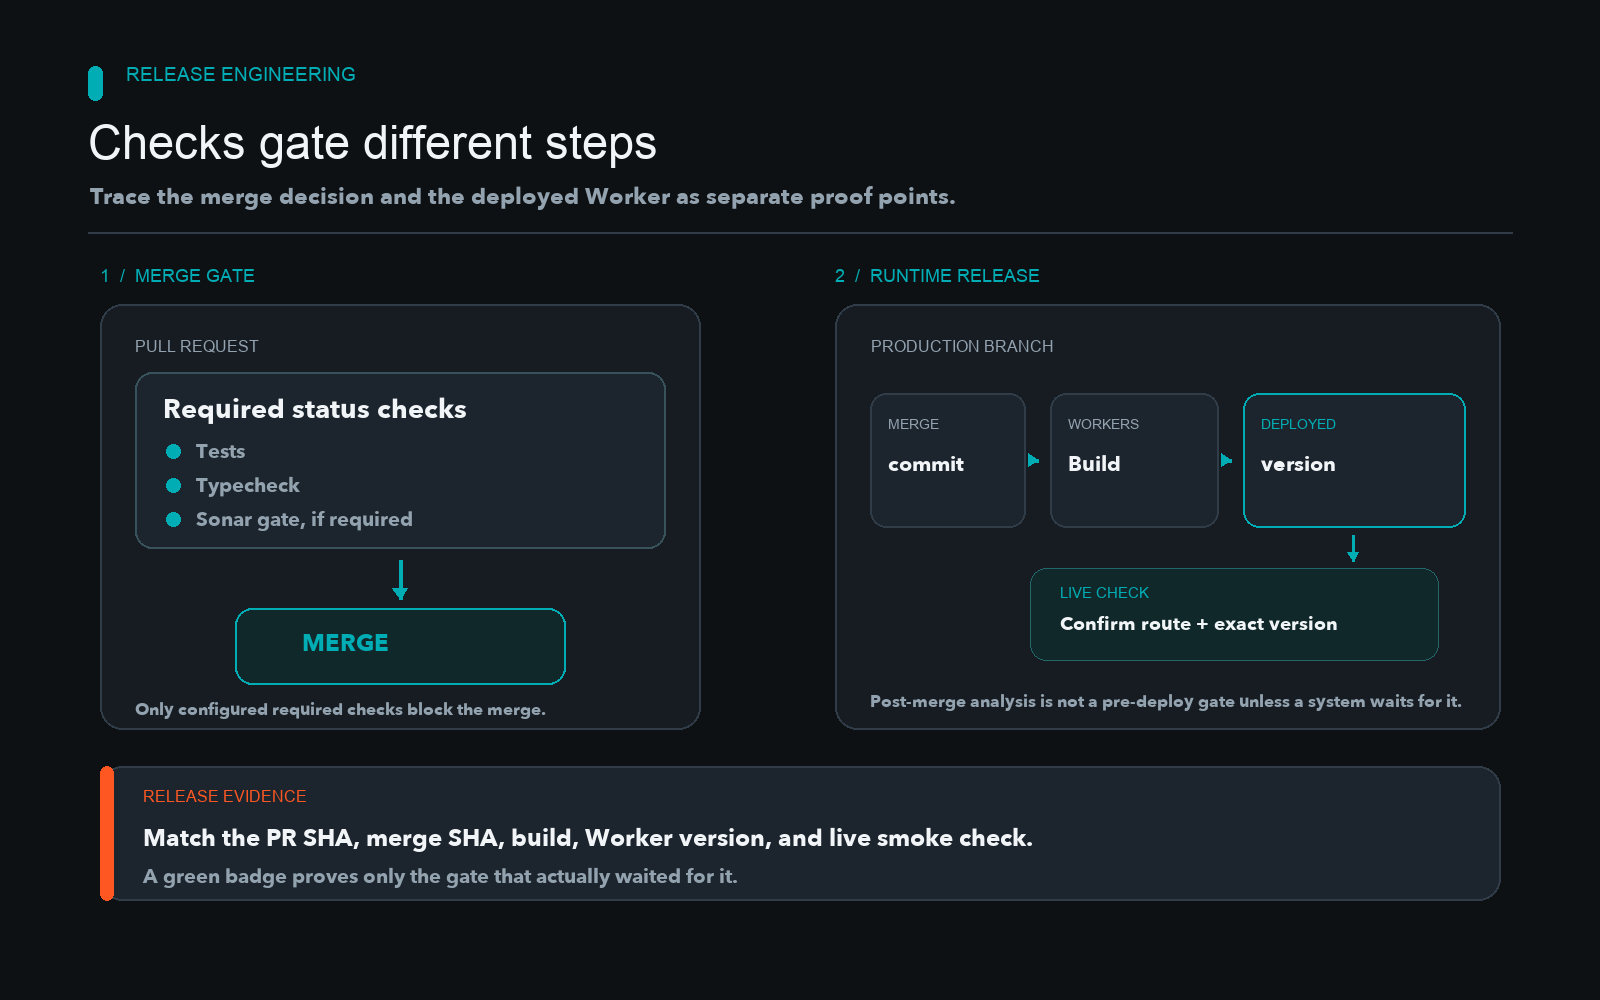
Learn how to separate CI validation from Cloudflare Worker deployments by enforcing branch protection, required status checks, and quality gates.
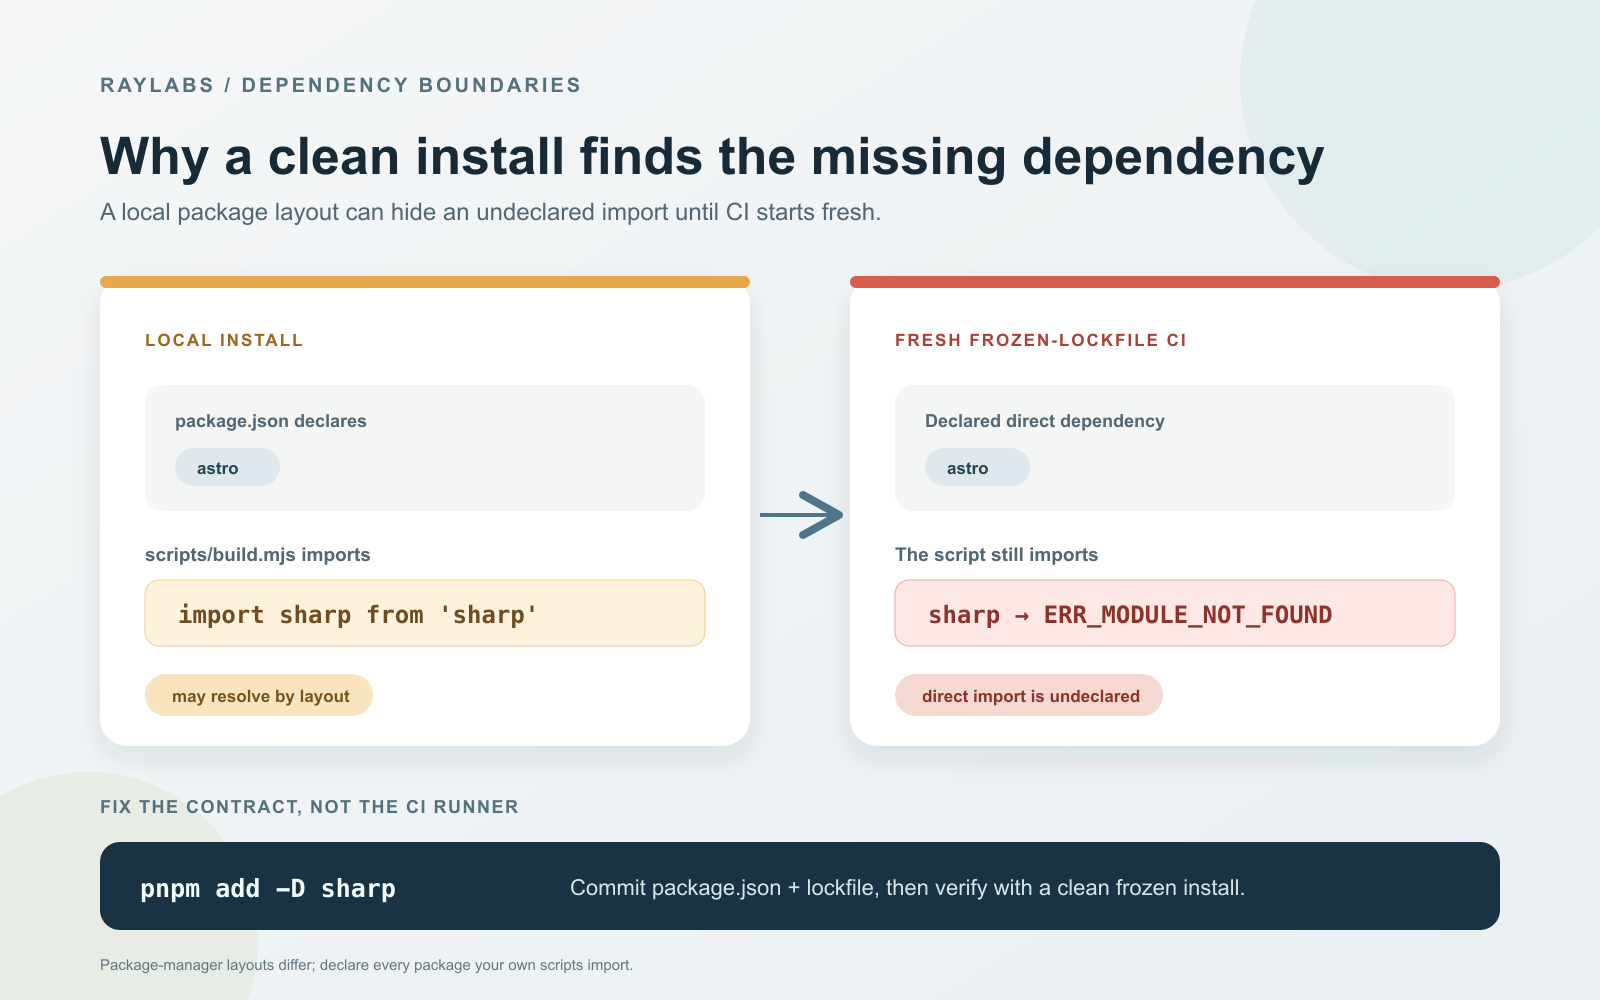
Learn how to diagnose and resolve ERR_MODULE_NOT_FOUND phantom dependency failures when transitioning from flat npm hoisting to strict pnpm in CI/CD pipelines.
Stop internal hostnames, staging URLs, and private network details from leaking into static-site HTML, JavaScript, feeds, source maps, and metadata.
Build one browser extension release pipeline with reproducible archives, store-specific APIs, safe credentials, bounded retries, and independent publication verification.
A practical pattern for keeping Android signing credentials and environment-specific values out of Git while making local and CI builds predictable.
A practical guide to designing small post-deploy sanity checks that verify the live release, critical dependencies, and rollback signals without duplicating CI.
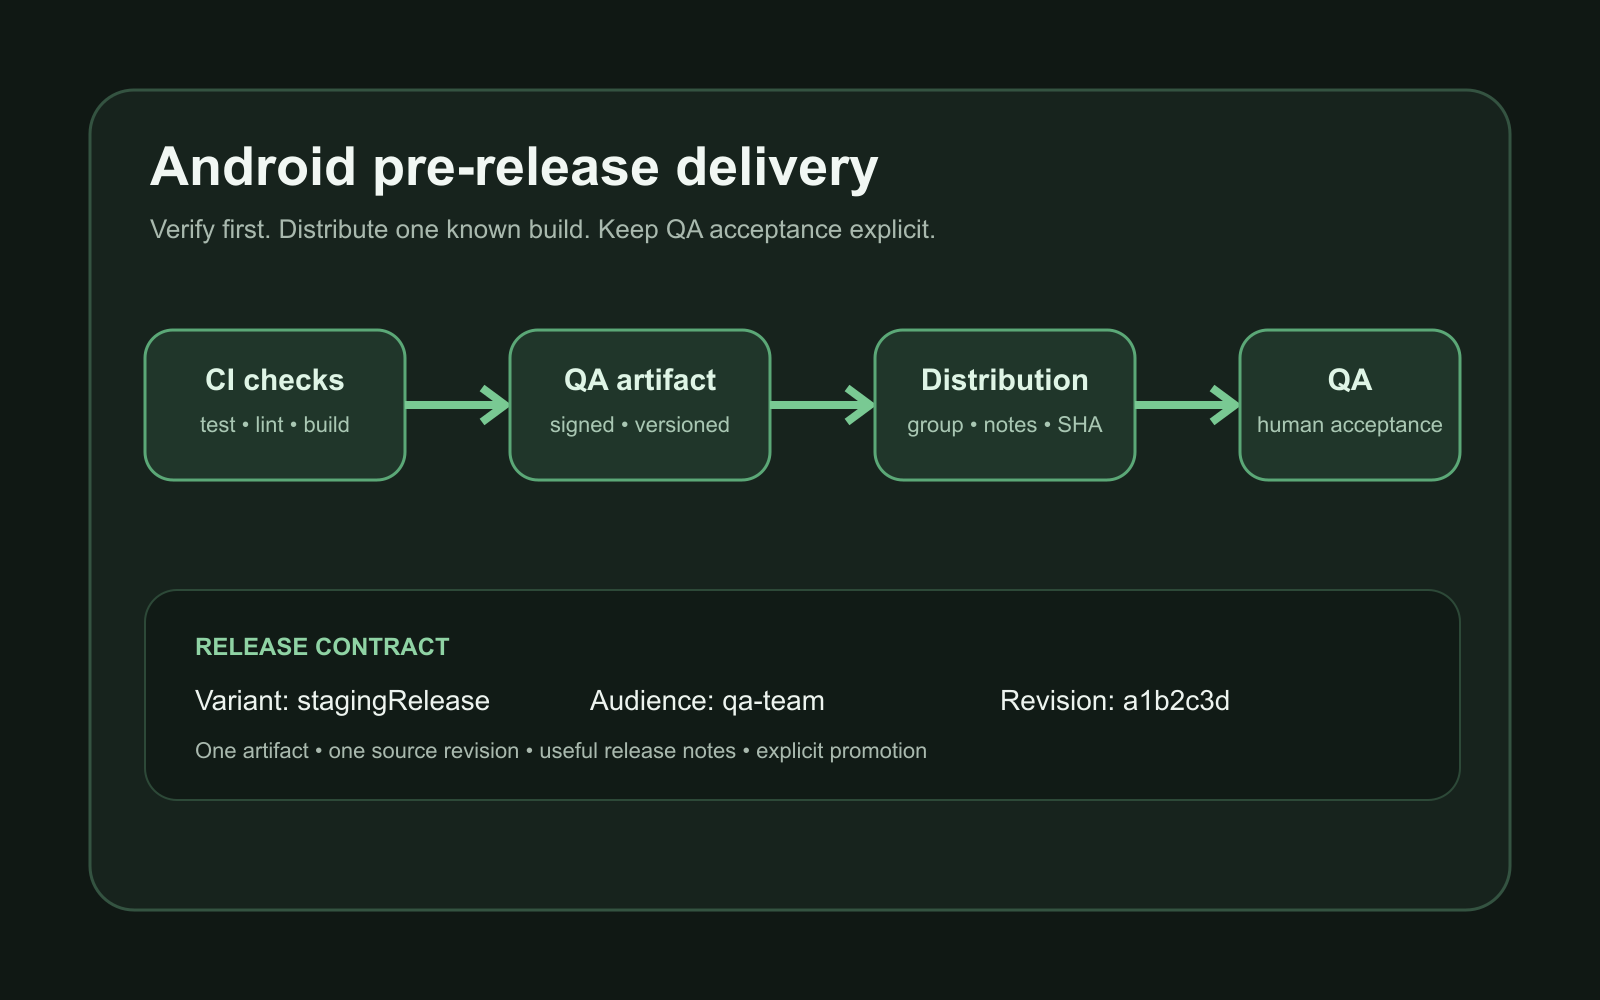
Build a repeatable Android pre-release pipeline with Firebase App Distribution, tester groups, release notes, CI gates, and variant-aware delivery.
AI publishing gets safer when repository schemas, local validation, CI, deploy checks, and live verification form one explicit chain.
A practical technical guide for setting up a reproducible Android CI workflow using GitHub Actions and Gradle, focusing on caching strategies, test execution boundaries, and failure diagnosis.
A practical software architecture review checklist for finding production risk across boundaries, data, failure modes, security, observability, delivery, and ownership.
Learn how to speed up Node.js CI and template deployments with reproducible installs, lockfile-aware dependency caching, and zero-build runtime patterns.
Learn how to clean generated build artifacts safely in CI by separating disposable workspace output from caches and release artifacts, then verifying the pipeline from a clean checkout.