OAuth Integration Delete Stored Tokens KV Data Deletion
Learn how to handle OAuth integration data deletion for KV-backed applications, covering local records, provider revocation, repeated requests, and failure isolation.
Production architectural patterns, system design, data modeling, reliability engineering, and decoupled service orchestration.
Sustainable engineering systems require rigorous architectural boundaries, explicit failure modes, and resilient data flow. This topic dissects clean architecture principles, state machine design, database migrations, distributed reliability, and fail-closed engineering gates. Discover patterns for building decoupled, observable software systems that scale without technical debt.
Learn how to handle OAuth integration data deletion for KV-backed applications, covering local records, provider revocation, repeated requests, and failure isolation.
Learn how to retry scheduled publishing after failures without double-publishing by separating attempt status, success streaks, and trial admission with source cooldowns and expiry bounds.
Learn how to separate endpoint discovery via RFC 9728 and RFC 8414 from strict runtime JWT validation using RFC 8725 best practices, preventing token-type confusion and audience bypasses.
Learn how to handle mid-batch crashes during API polling by separating retrieval progress from side-effect completion and tracking per-item recovery evidence.
Learn how to keep a Cloudflare Worker image selection pipeline running when an HTTP response stream fails after headers return successfully.
Learn how to build a read-only operator dashboard for serverless publishing workflows on Cloudflare Workers without risking duplicate runs.
Learn how to preserve fallback search semantics when a requested query equals the fallback query, preventing strict relevance thresholds from rejecting valid candidate images.
Learn how to build a bounded failover chain for Gemini API keys that handles both quota exhaustion and transient server errors without leaking secrets.
Learn how to build a knowledge base bot that safely abstains when its local index lacks matching answers, distinguishing related passages from true evidence.
Learn how an editorial publishing pipeline keeps internal engineering provenance in private inputs while validating only eligible public citation metadata before any site commit.
Learn how to select a specific queued article revision using a validated path without widening your bounded queue scan or bypassing review guards.
Learn how to configure separate Google Cloud projects for Gemini API keys to handle rate-limit exhaustion and ensure your serverless workflow fails over correctly.
Examine why manual parent workflows fail at child boundaries when custom instance identifiers violate downstream prefix assumptions, and learn how to validate platform IDs safely.
Learn how to prevent unnecessary LLM generation retries by normalizing minor Markdown formatting variations before schema validation.
Learn how to prevent automated publication asset discovery tools from mistaking literal Markdown image examples inside code blocks for real media dependencies.
Fix a technical article validator bug that rejected valid tilde-fenced code blocks by reusing the core Markdown fence reader.
Learn how to update quick-solution validators and prose-masking routines to recognize matching backtick or tilde fences of any length.
Understand why hashing raw file bytes produces a different value than Git and the GitHub API, explore UTF-8 byte length versus string length, and learn when to use a separate digest for application integrity.
Build a local-first error log with bounded retention, secret redaction, and user-initiated reporting for plugin ecosystems that prohibit client telemetry.
Learn how to select the newest draft revision in a bounded workflow queue by sorting descending revisions before path tie-breaks.
Preserve structured field errors from HTTP 422 responses while bounding diagnostics, redacting credentials, and keeping provider payloads untrusted.
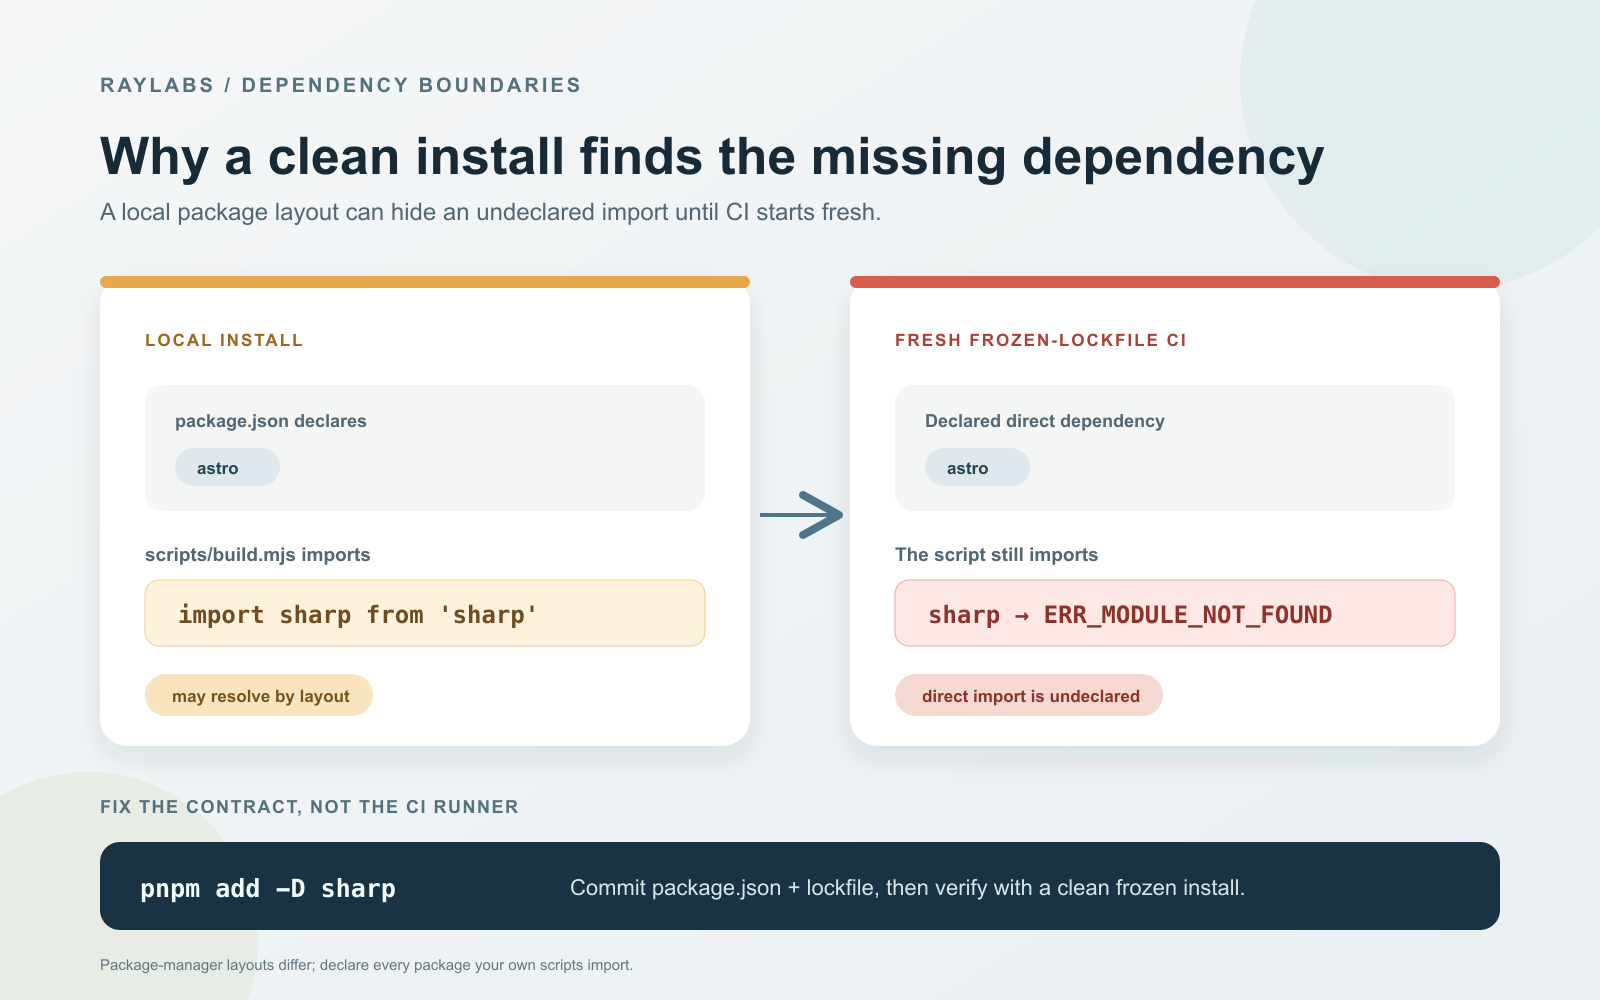
Learn how to diagnose and resolve ERR_MODULE_NOT_FOUND phantom dependency failures when transitioning from flat npm hoisting to strict pnpm in CI/CD pipelines.
Learn how to avoid regular expression denial of service vulnerabilities in lightweight Markdown frontmatter parsers by replacing complex regex with bounded line scans.
A practical guide to diagnosing, remediating, and maintaining a zero-defect SonarCloud Quality Gate Rating A across static web applications and frontend architectures without sacrificing developer velocity.
Learn how to design self-clearing kill switches that prevent transient outages from turning into persistent pager events, alongside human-readable failure reports that replace raw JSON dumps.
Learn how to calculate true scheduled publishing reliability by anchoring your denominator to cron slots and verifying user-visible outcomes rather than trigger attempts.
A practical architecture for automating SaaS workflows without a public API using supported boundaries, browser adapters, idempotency, verification, and manual fallback.
Learn how to prevent deployment failures in Git-backed publishing systems when unrelated synchronization commits occur during the publication process.
A practical, problem-led guide for developers on inspecting phishing attempts, verifying senders, hardening MFA, and auditing OAuth permissions.
Learn how to build a safe, isolated Linux and Kali Linux laboratory in VirtualBox, focusing on network modes, safe snapshot workflows, and security boundaries.
Get instant updates when new Software Architecture engineering deep-dives, benchmarks, and architecture guides are published.